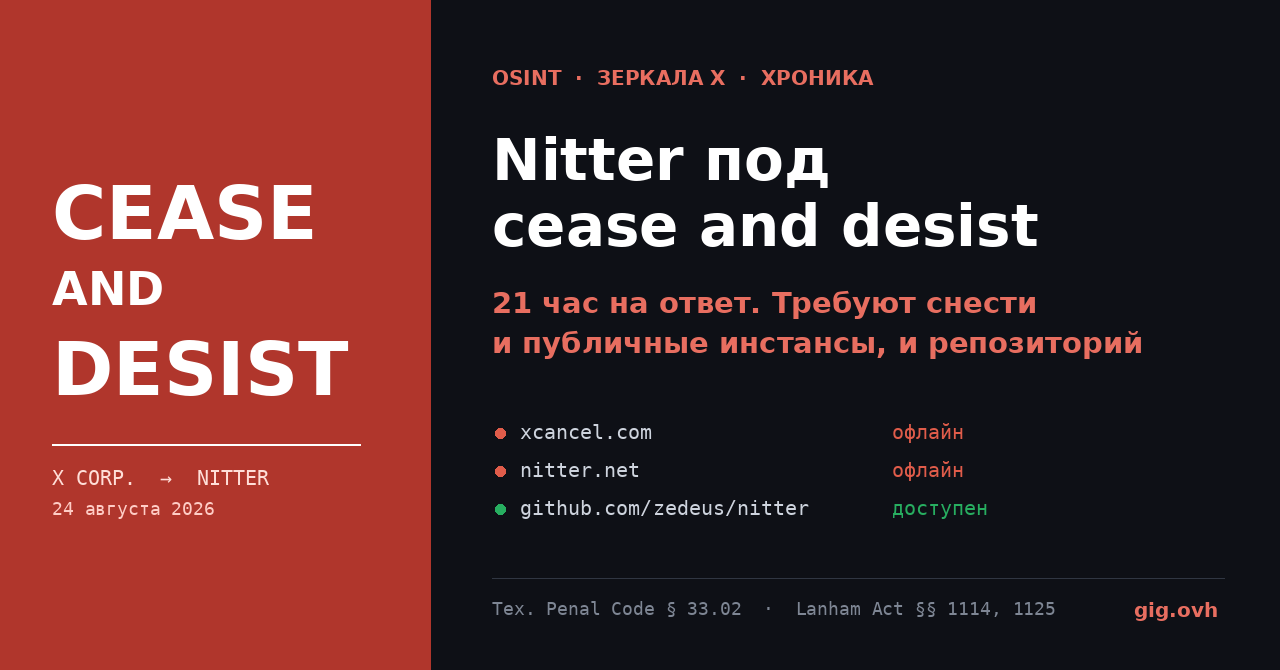
On August 24, 2026, the lawyers of X Corp. sent letters demanding to stop the violations — to the Nitter project, its public mirrors and services built on its code, including XCancel. By the morning of August 26, nitter.net and xcancel.com were unresponsive. A developer going by the handle zedeus confirmed receiving the letter and declined to comment: “I’m seeking legal advice and won’t be commenting further.”
For forum readers, this isn’t news about a social network. Nitter served posts from X without an account, without JavaScript, and with a ready RSS feed for every profile, so it wound up in readers, monitoring tools, and Home Assistant automations. Let’s unpack what’s in the letter, how this story differs from X’s past raids on scrapers, and what it means for the owners of their instances.
A step-by-step look over a day and a half
August 24, around 8:00 PM EST. Letters go out to recipients. The letter’s demand is quoted by zedeus himself: “demanding a permanent takedown of Nitter instances and the project’s repository” — they’re asking not only to delete mirrors but also the original code on GitHub.
August 25, 5:00 PM EST. The deadline from the letter: according to TechCrunch, which reviewed the document, the window to respond was about 21 hours.
August 25, daytime. The first public symptom wasn’t a legal document, but a bug report: in issue #1442 they report all public instances returning a single error — Instance has been rate limited.
August 26. Both flagship domains are silent. The repository github.com/zedeus/nitter remains in place: 13.1k stars, not archived, and the demand to delete it has not been fulfilled.
The letter is not a lawsuit yet. X Corp. stated the demand and its grounds; the court has not reviewed them. Next comes an analysis of what they reference, not a proclamation of who is right.
Two tracks in the letter
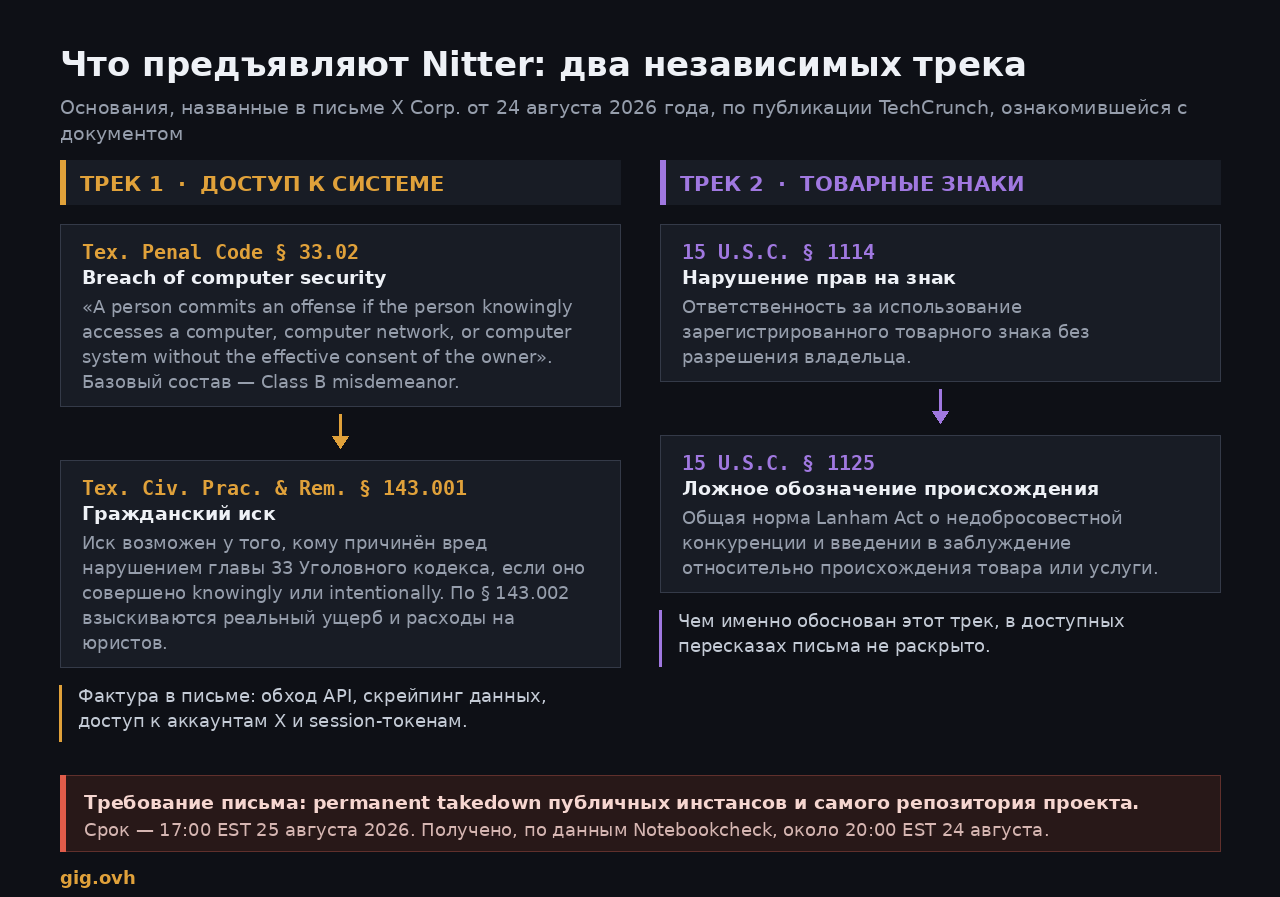
Diagram based on the Texas Penal Code Chapter 33, the Texas Civil Practice & Remedies Code Chapter 143, and the description in TechCrunch
First track — Texas. § 33.02 of the Penal Code broadly defines the offense: “A person commits an offense if the person knowingly accesses a computer, computer network, or computer system without the effective consent of the owner.” The key term is effective consent: under § 33.01(12) consent is invalid when access is used beyond what the owner has authorized. The criminal provision is paired with § 143.001 Civil Practice & Remedies Code, which gives a right to civil action if the violation of Chapter 33 is committed knowingly or intentionally, and § 143.002 allows recovering actual damages and attorney’s fees.
Second track — trademarks, §§ 1114 and 1125 of the Lanham Act. Exactly how this is argued isn’t disclosed in available summaries of the letter, and I won’t speculate for X’s lawyers.
Why Bright Data isn’t a shield here
In discussions, people immediately recall X Corp. v. Bright Data: in May 2024, Judge William Alsup (N.D. Cal., No. C 23-03698 WHA) rejected X’s claims against a scraper, noting that prohibiting scraping of publicly available data via a user agreement clashes with the preeminent federal copyright. The claim that “scraping public data is legal” has since circulated on forums as a universal defense.
Nitter’s position is different. Since 2024 it has not operated anonymously — the README states explicitly: “Running a Nitter instance now requires real accounts, since Twitter removed the previous methods.” Each active instance maintains real X accounts and their session tokens. That is the issue the letter hooks onto: this is not about “we read a public page,” but about access to accounts and session tokens bypassing the API. The debate about public data and the debate about effective consent under someone else’s sessions are different disputes.
Previously, running your own Nitter meant “set up a container.” Now it means “get battle-tested X accounts your server can use” — and this detail is what turns homebrew into the scenario X describes as a violation. The letters were sent not only to the project but also to operators of individual mirrors.
Where else is this spelled out
A dead RSS feed is dangerous because it gives no signal: a reader simply stops showing items, making it look like “the source published nothing.”
Check your readers’ configs, configuration.yaml for Home Assistant, docker-compose.yml, and monitoring scripts:
grep -rIn --exclude-dir=.git -E 'nitter|xcancel' \\
  /opt /srv /etc ~/.config 2>/dev/null
The liveliness of a particular feed is easiest to verify by the HTTP status code — anything not 200 isn’t cured by a reader:
curl -sS -o /dev/null -w '%{http_code}\n' https://xcancel.com/<profile>/rss
For archiving a single post as proof of a mirror, a public page wasn’t enough: an open page doesn’t confirm anything. A working approach is a public archiver with an independent timestamp (Wayback Machine, archive.today) and a saved image URL.
Nitter didn’t go down due to a technical block, but due to a letter for which there is neither a fork nor a proxy. A tool with a single maintainer and a legal status of “not yet litigated” shouldn’t be relied on as the basis of a production pipeline.
A related forum topic — public Certificate Transparency logs: there, data is released officially and permanently.
Sources
- X sends cease-and-desist to open source project Nitter — TechCrunch, 25.08.2026
- XCancel gets taken down as X Corp sends cease-and-desist letter — Notebookcheck
- Quote from zedeus about the letter — Pixel Envy
- Issue #1442: All public nitter instances do not work
- Texas Civil Practice & Remedies Code, ch. 143
- Texas Penal Code, ch. 33
- X loses lawsuit against Bright Data — CNBC, 10.05.2024
- Nitter project repository
Who among Nitter or XCancel was in your active setup — what broke specifically and how are you closing the task now? And specifically to those who ran an instance with real accounts: are you deleting them or waiting?